

Private AI deployment
Choose where the model runs, what it can access and how your team operates it.
Identify the user before allowing access to the application or its data.
Make the data boundary explicit.
Identity and permissions decide who can use the system.
An example deployment, explored one layer at a time.
Work behind the service
Explore the journal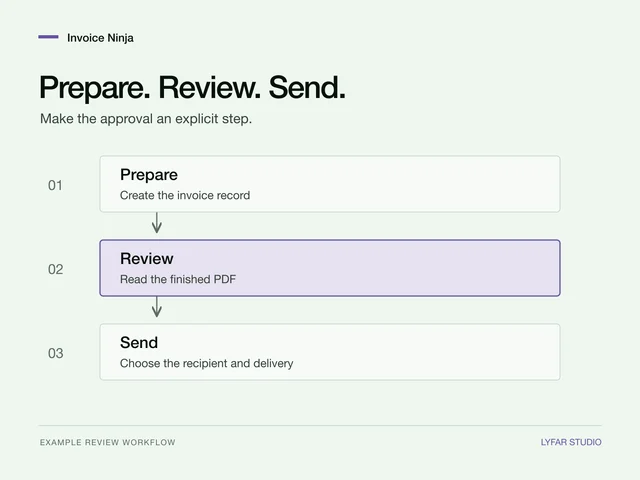
From the first conversation to the handover.
Set the boundary
Establish data access, retention, connectivity and operating requirements.
Compare the options
Assess local models and controlled infrastructure against the actual workload.
Test and hand over
Check the chosen deployment and document its operation and limits.
Begin with the data boundary
Private deployment can mean different things: inference on a device, a service on your network or a controlled hosted environment. We define the requirement in practical terms before choosing an architecture.
What may leave the environment? Who can access the records? What needs to be retained? Does the system need to work without an external connection? Those answers shape the design.
Test the workload on the intended setup
A model fitting in memory is only a starting point. We assess response quality, latency, concurrency and resource use on the actual task. Some workloads suit a local model; others need a different model or a hybrid arrangement.
Operations belong in the scope
Installation, access control, updates, monitoring and recovery need an owner. The handover should make the service understandable to the people responsible for running it.
A private deployment does not by itself establish regulatory compliance. Specific security and compliance requirements need to be identified and reviewed with the organisation’s responsible specialists.
Bring the task and the data constraints. A focused feasibility check can establish whether the proposed setup is useful before a wider rollout.
A few things you might be wondering.
Does private automatically mean secure?
No. Access control, updates, logging and operational practices still need to be designed and maintained.
Can it run locally?
We assess local deployment against the models, hardware and workload required. It is an option to test, not a default promise.
Tell us what you're building.
Bring the task, the people using it and the systems it needs to work with. We'll define the scope and the next useful step.
Discuss your project